Cold Chain Cyberattack: Six Lessons for Every Enterprise IT Leader
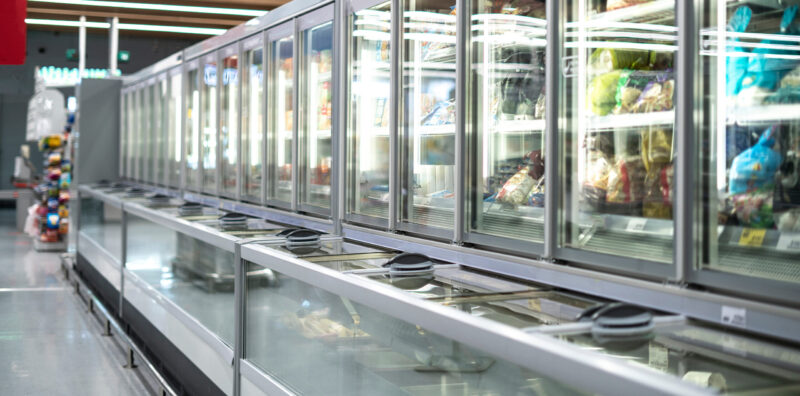
Recent cyberattacks on refrigeration and freezer systems in Europe expose easily exploitable vulnerabilities. The bigger story goes beyond the cold chain. Here are six takeaways for your supply chain.
In Europe, attackers reached internet-connected refrigeration controllers, many of them older units with outdated firmware and, in some cases, default passwords, and remotely forced them into overnight heating cycles. Investigations are still ongoing, and no one has claimed responsibility, but the bigger story goes beyond refrigeration. It says something about how supply chain and logistics companies manage enterprise technology.
The flaws had been publicly disclosed months earlier. Patching should now be measured in hours after release, not days or weeks.
Here are the lessons every enterprise IT leader should take from these incidents, whatever their industry:
- Your attack surface is anything with a network connection, not just what IT bought. These controllers were most likely bought by facilities teams or installed by contractors. They were probably outside IT’s inventory, and so outside its security program. Most enterprises have the same blind spot in building systems, badge readers, cameras, HVAC, and plant equipment.
- Your vendors are part of your perimeter. Remote access was added so contractors could service equipment more cheaply, and that access became the way in. Every third-party connection is a security decision, whether anyone treated it as one.
- Ownership failed here, not knowledge. The vulnerabilities were public, and the fixes were known. What was missing was clear accountability for devices that sit between IT, operations, and vendors. If no one owns an asset, no one patches it.
- Cyber risk is now an operational and physical risk. Nothing was stolen here. The damage came from destroyed inventory, store closures and, in France, fires. That changes who needs to be at the table. Boards, COOs, and risk teams should see these exposures in business terms, and continuity plans should cover losing physical operations, not only losing systems.
- Treat someone else’s incident as your early warning. This started in one country, grew in scale, and spread across borders within weeks. Attackers test, learn, and expand. Organizations that work from the rule that anything using the network falls under IT’s control have an edge.
- Alerting and monitoring decide how fast you stop it. When common attacker tactics show up, is alerting in place, and does it reach a wide enough audience to stop them? Does the SOC analyst on shift at 0400 have the authority to quarantine without asking permission first? In a cyber incident, speed decides the outcome.
What to Ask Your Team
Every IT leader should put three questions to their team this week:
- Do we know every connected device in our operation, including the ones vendors manage?
- Which of them can be reached from the internet, and why?
- If one of them were manipulated overnight, how would we find out, and how fast?